01Discovery
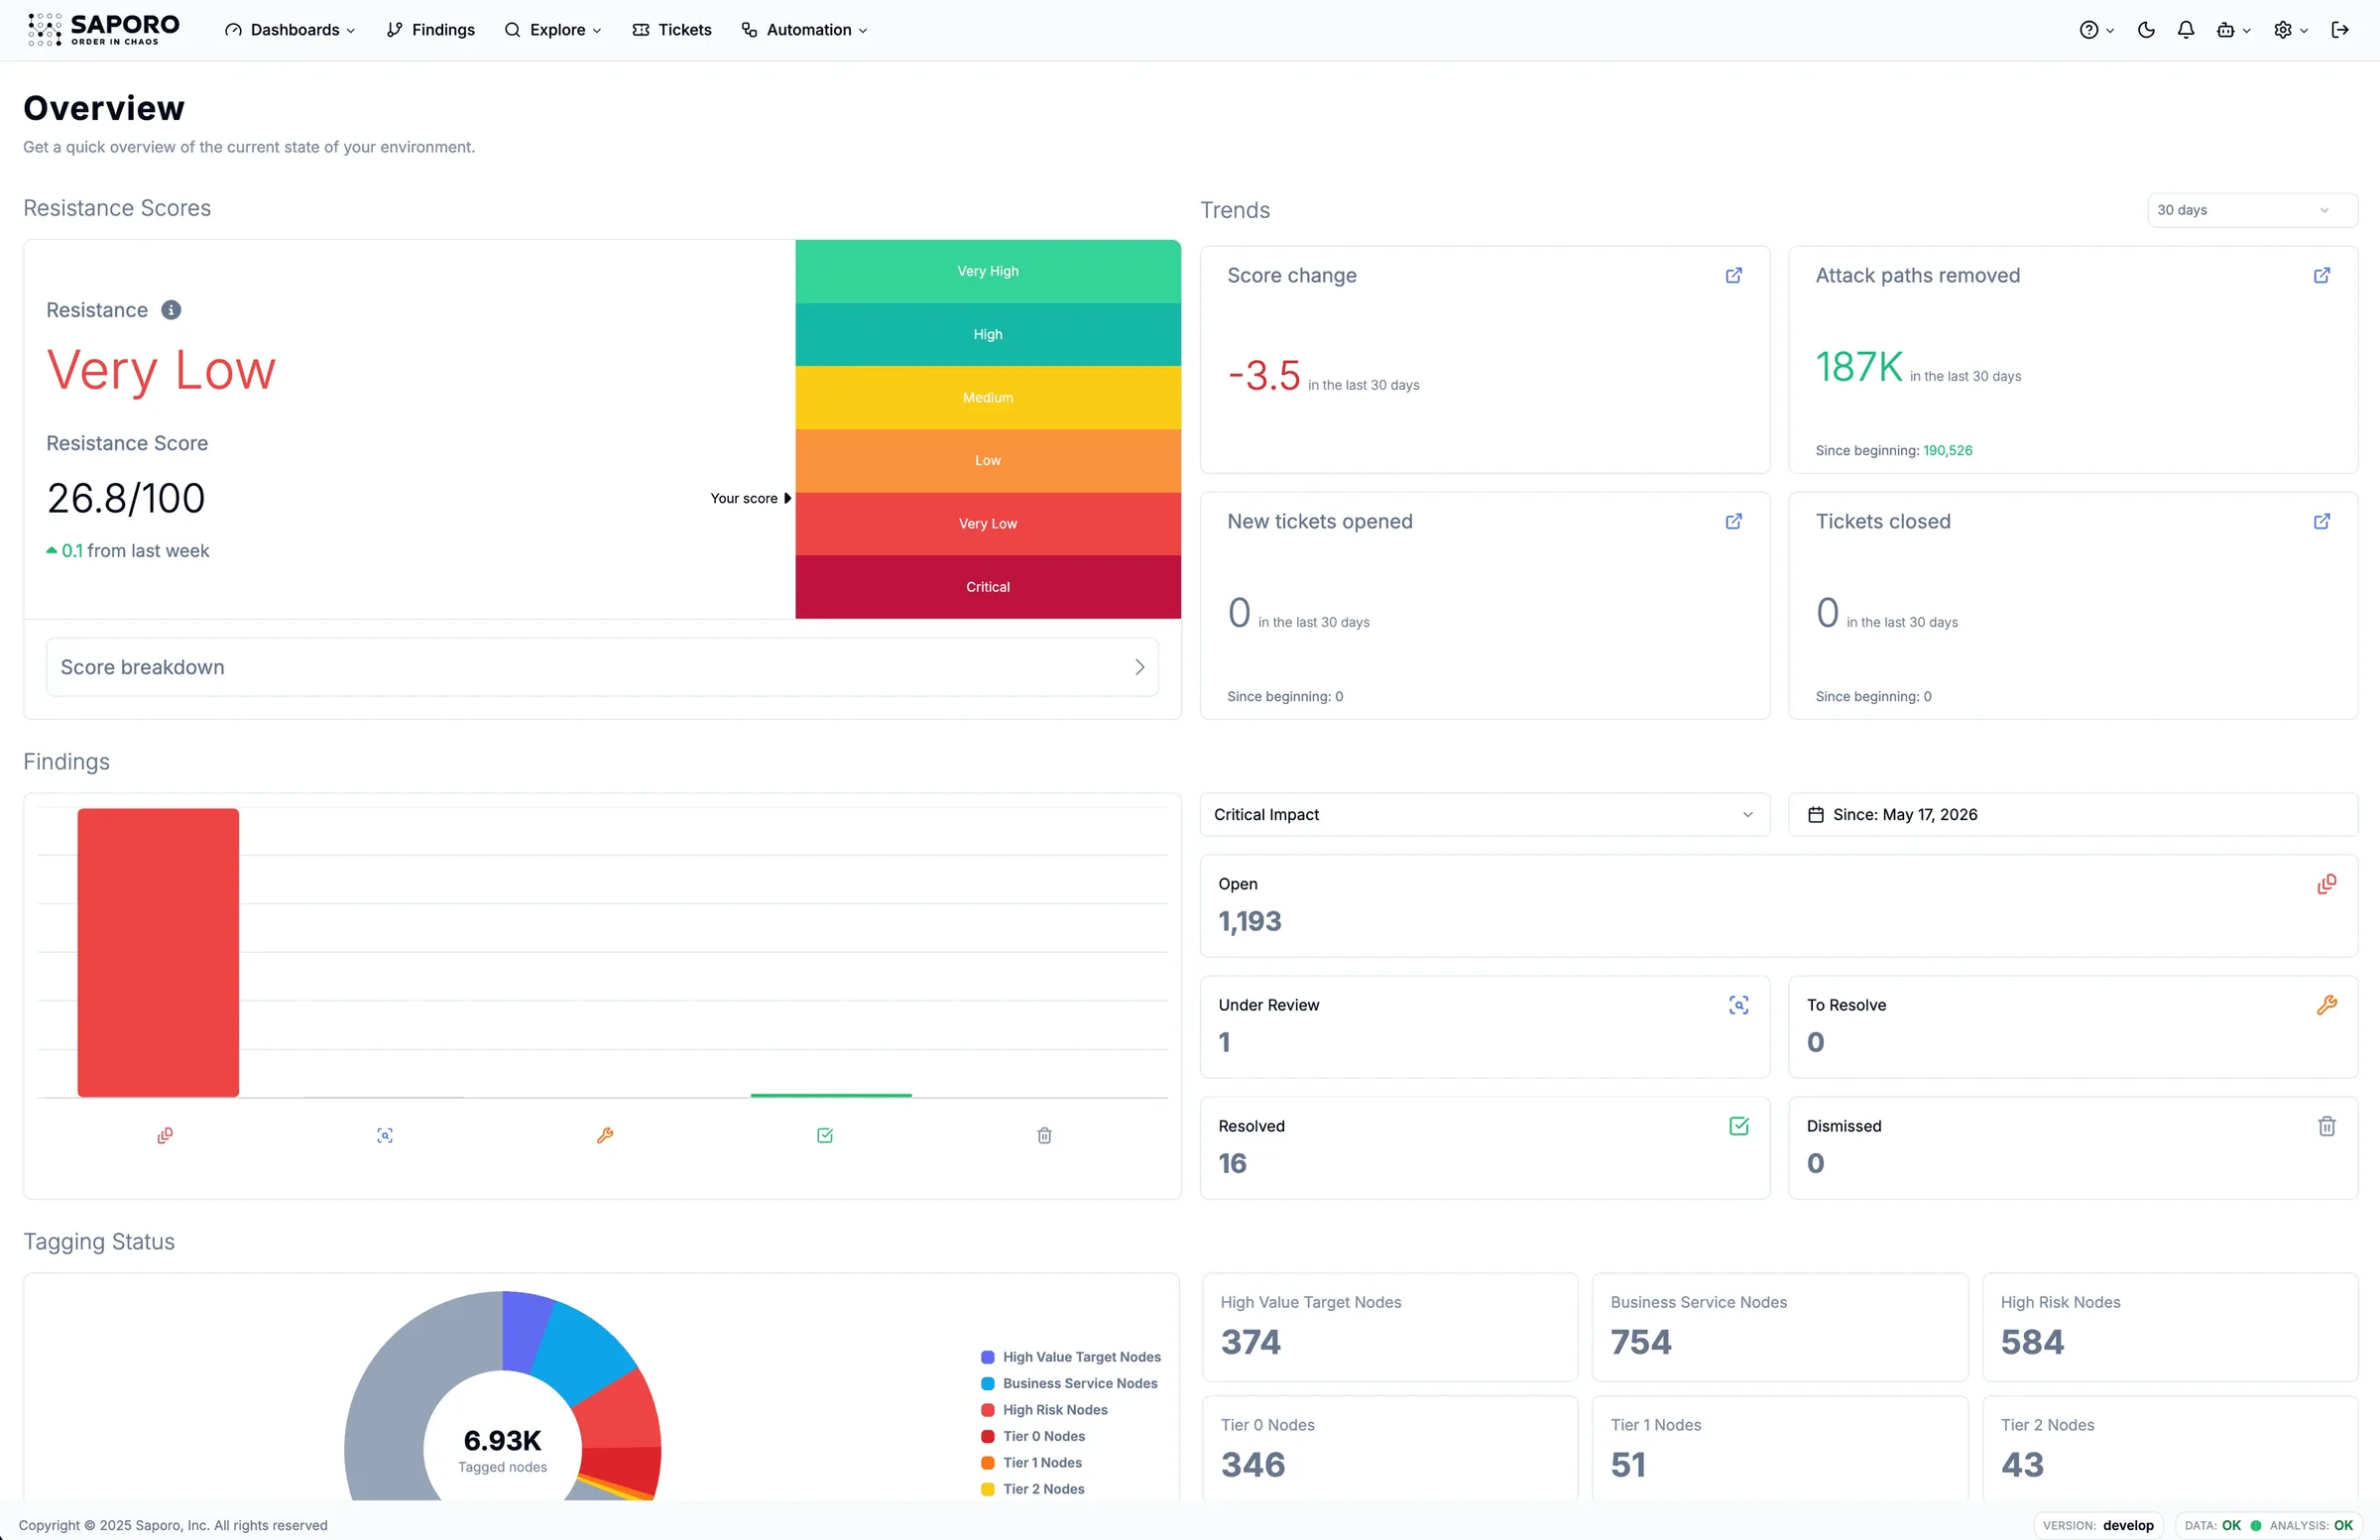
What can reach critical assets?
Map identities, permissions, and misconfigurations into the attack paths that matter across your hybrid environment.
What this unlocks
The exposures that create real attack opportunities.

Free identity exposure assessment
Map the attack paths that can reach critical assets and get an evidence-backed remediation roadmap. The assessment is free, agentless, and read-only, with prioritized results the same day.
Hybrid identity coverage
On-premise
Cloud and SaaS
The decisions your assessment answers
Map identities, permissions, and misconfigurations into the attack paths that matter across your hybrid environment.
What this unlocks
The exposures that create real attack opportunities.
Rank work by exploitability, propagation potential, and impact instead of treating every finding as equally urgent.
What this unlocks
The fixes that remove the most reachable risk across your environment.
Connect every finding to evidence, validation, and a clear remediation order your technical owners can act on.
What this unlocks
A pre-validated remediation backlog and an executive summary to act on.
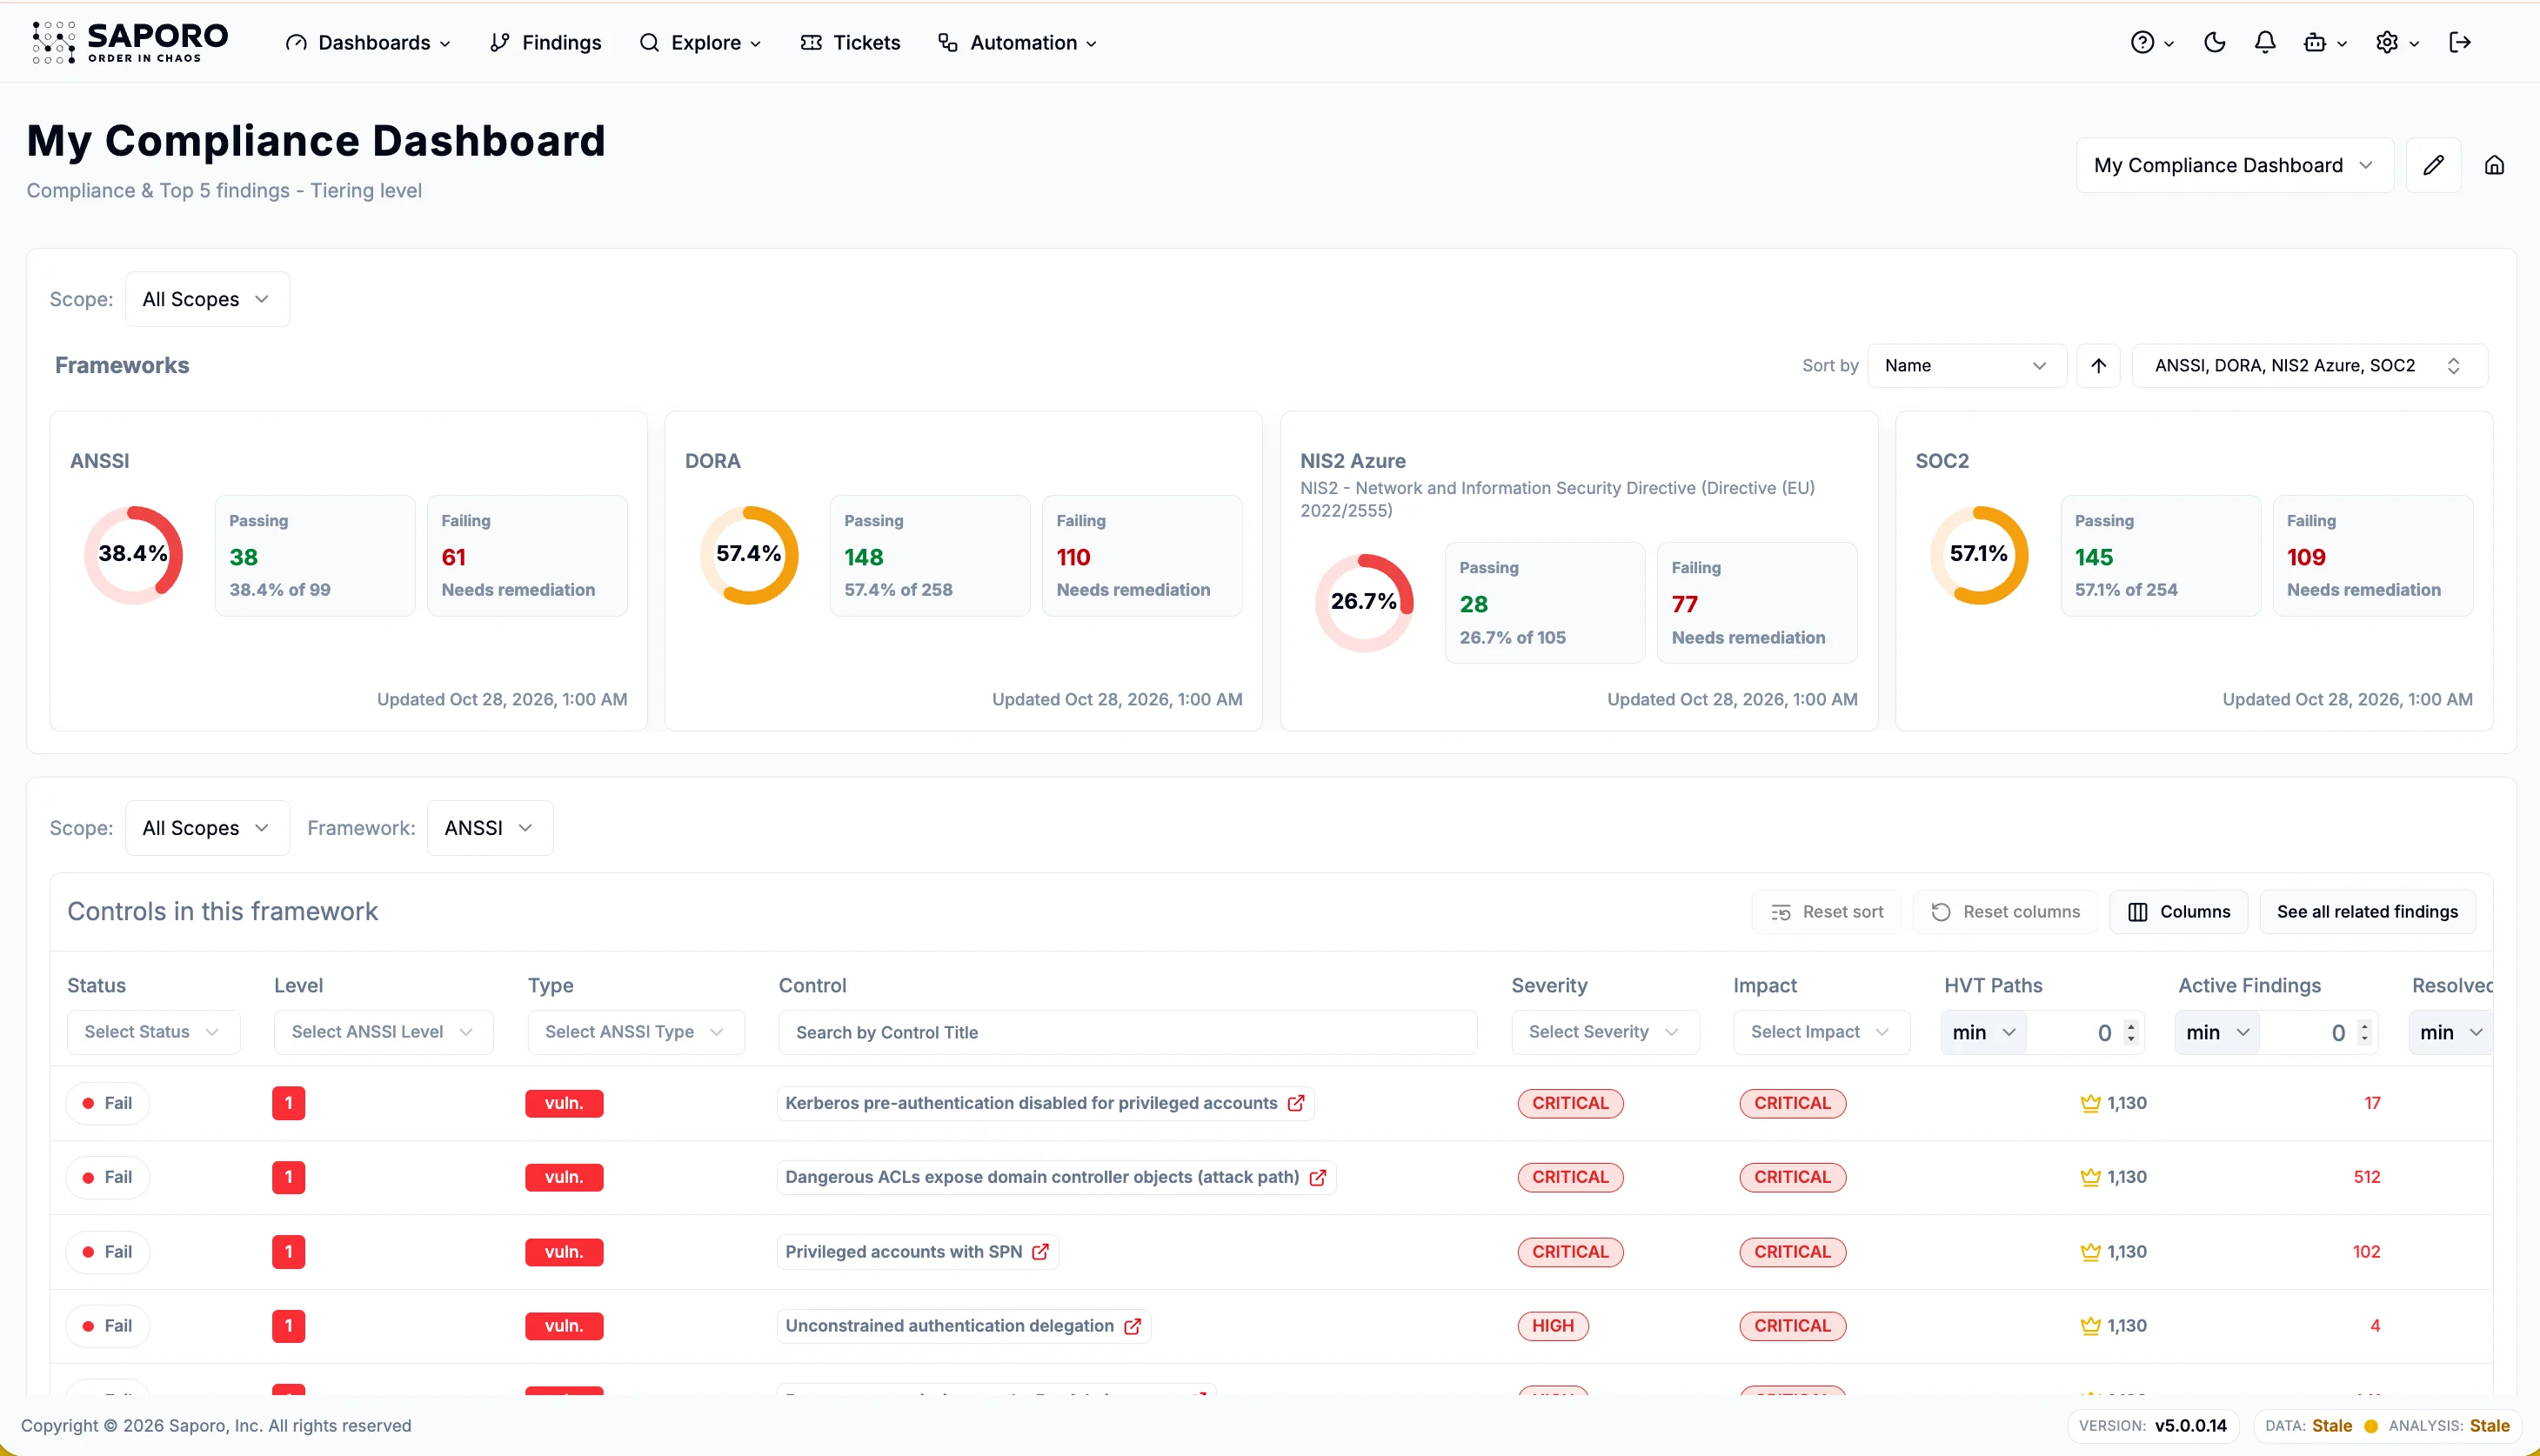
Compliance and tiering, backed by evidence
1,000+
built-in controls
Each finding connects technical remediation to measurable compliance progress.
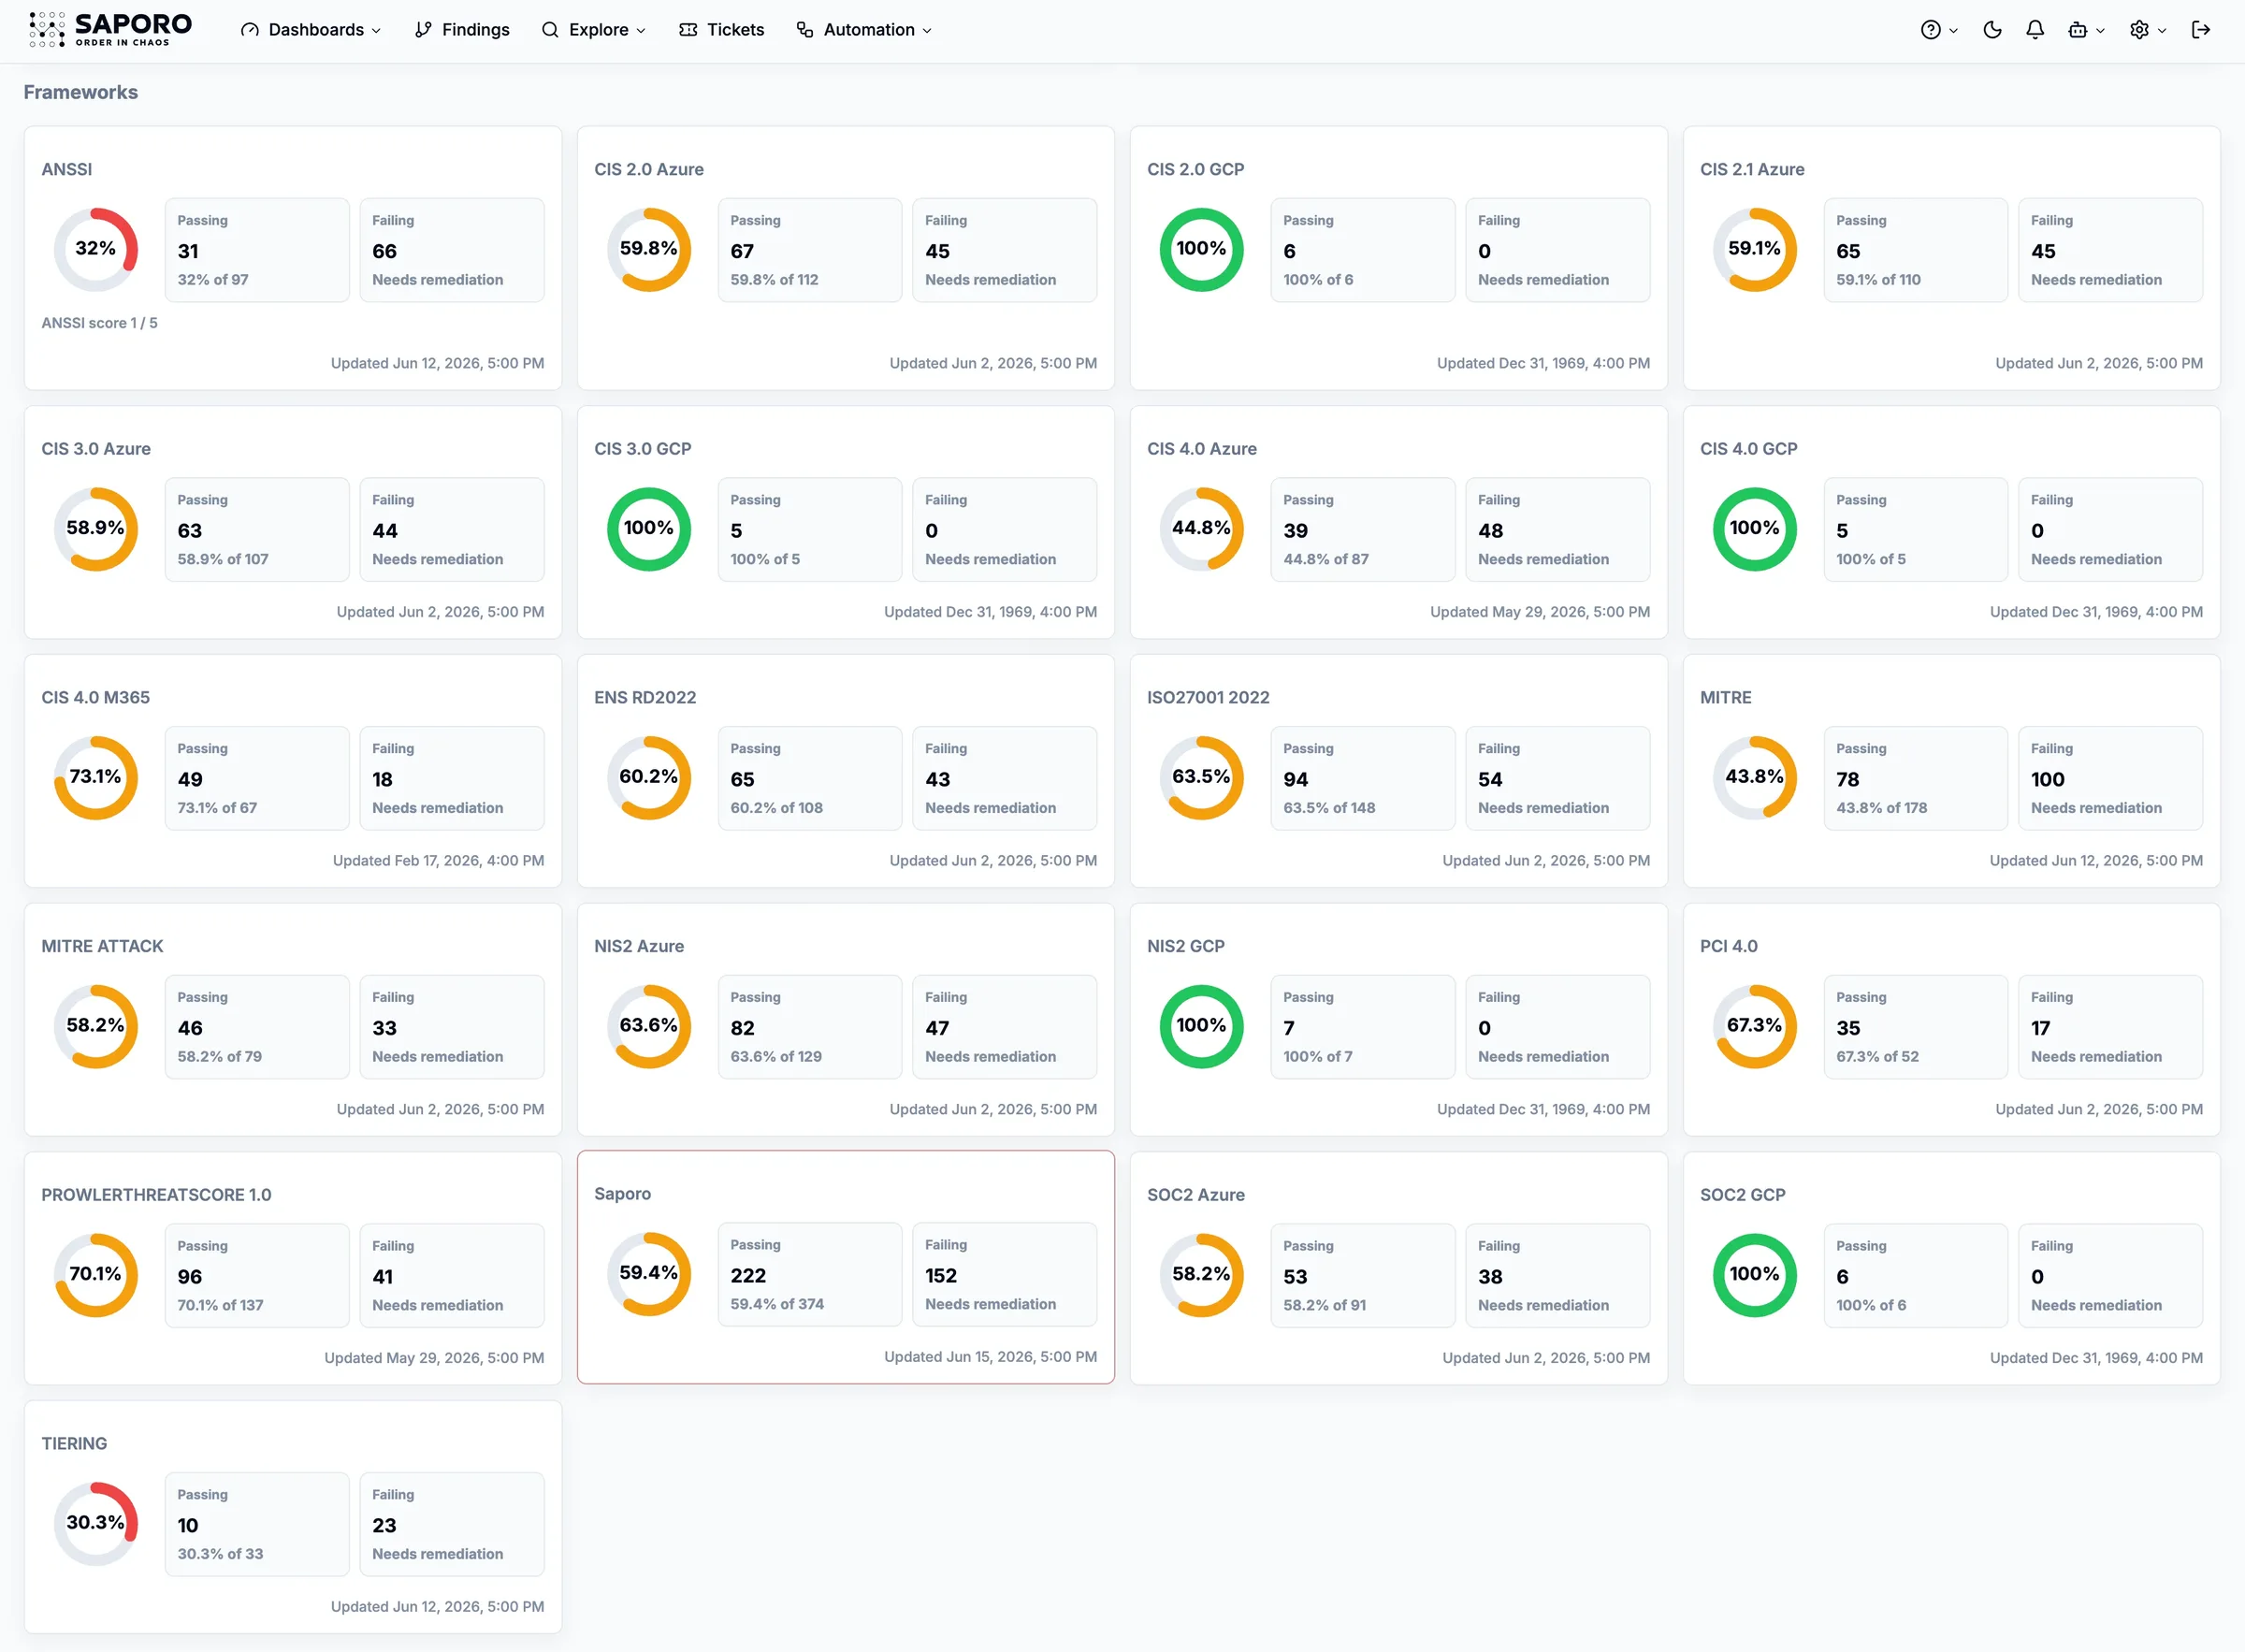
40+
frameworks covered
Including ANSSI, CIS, ISO 27001, NIS2, MITRE ATT&CK and Microsoft.
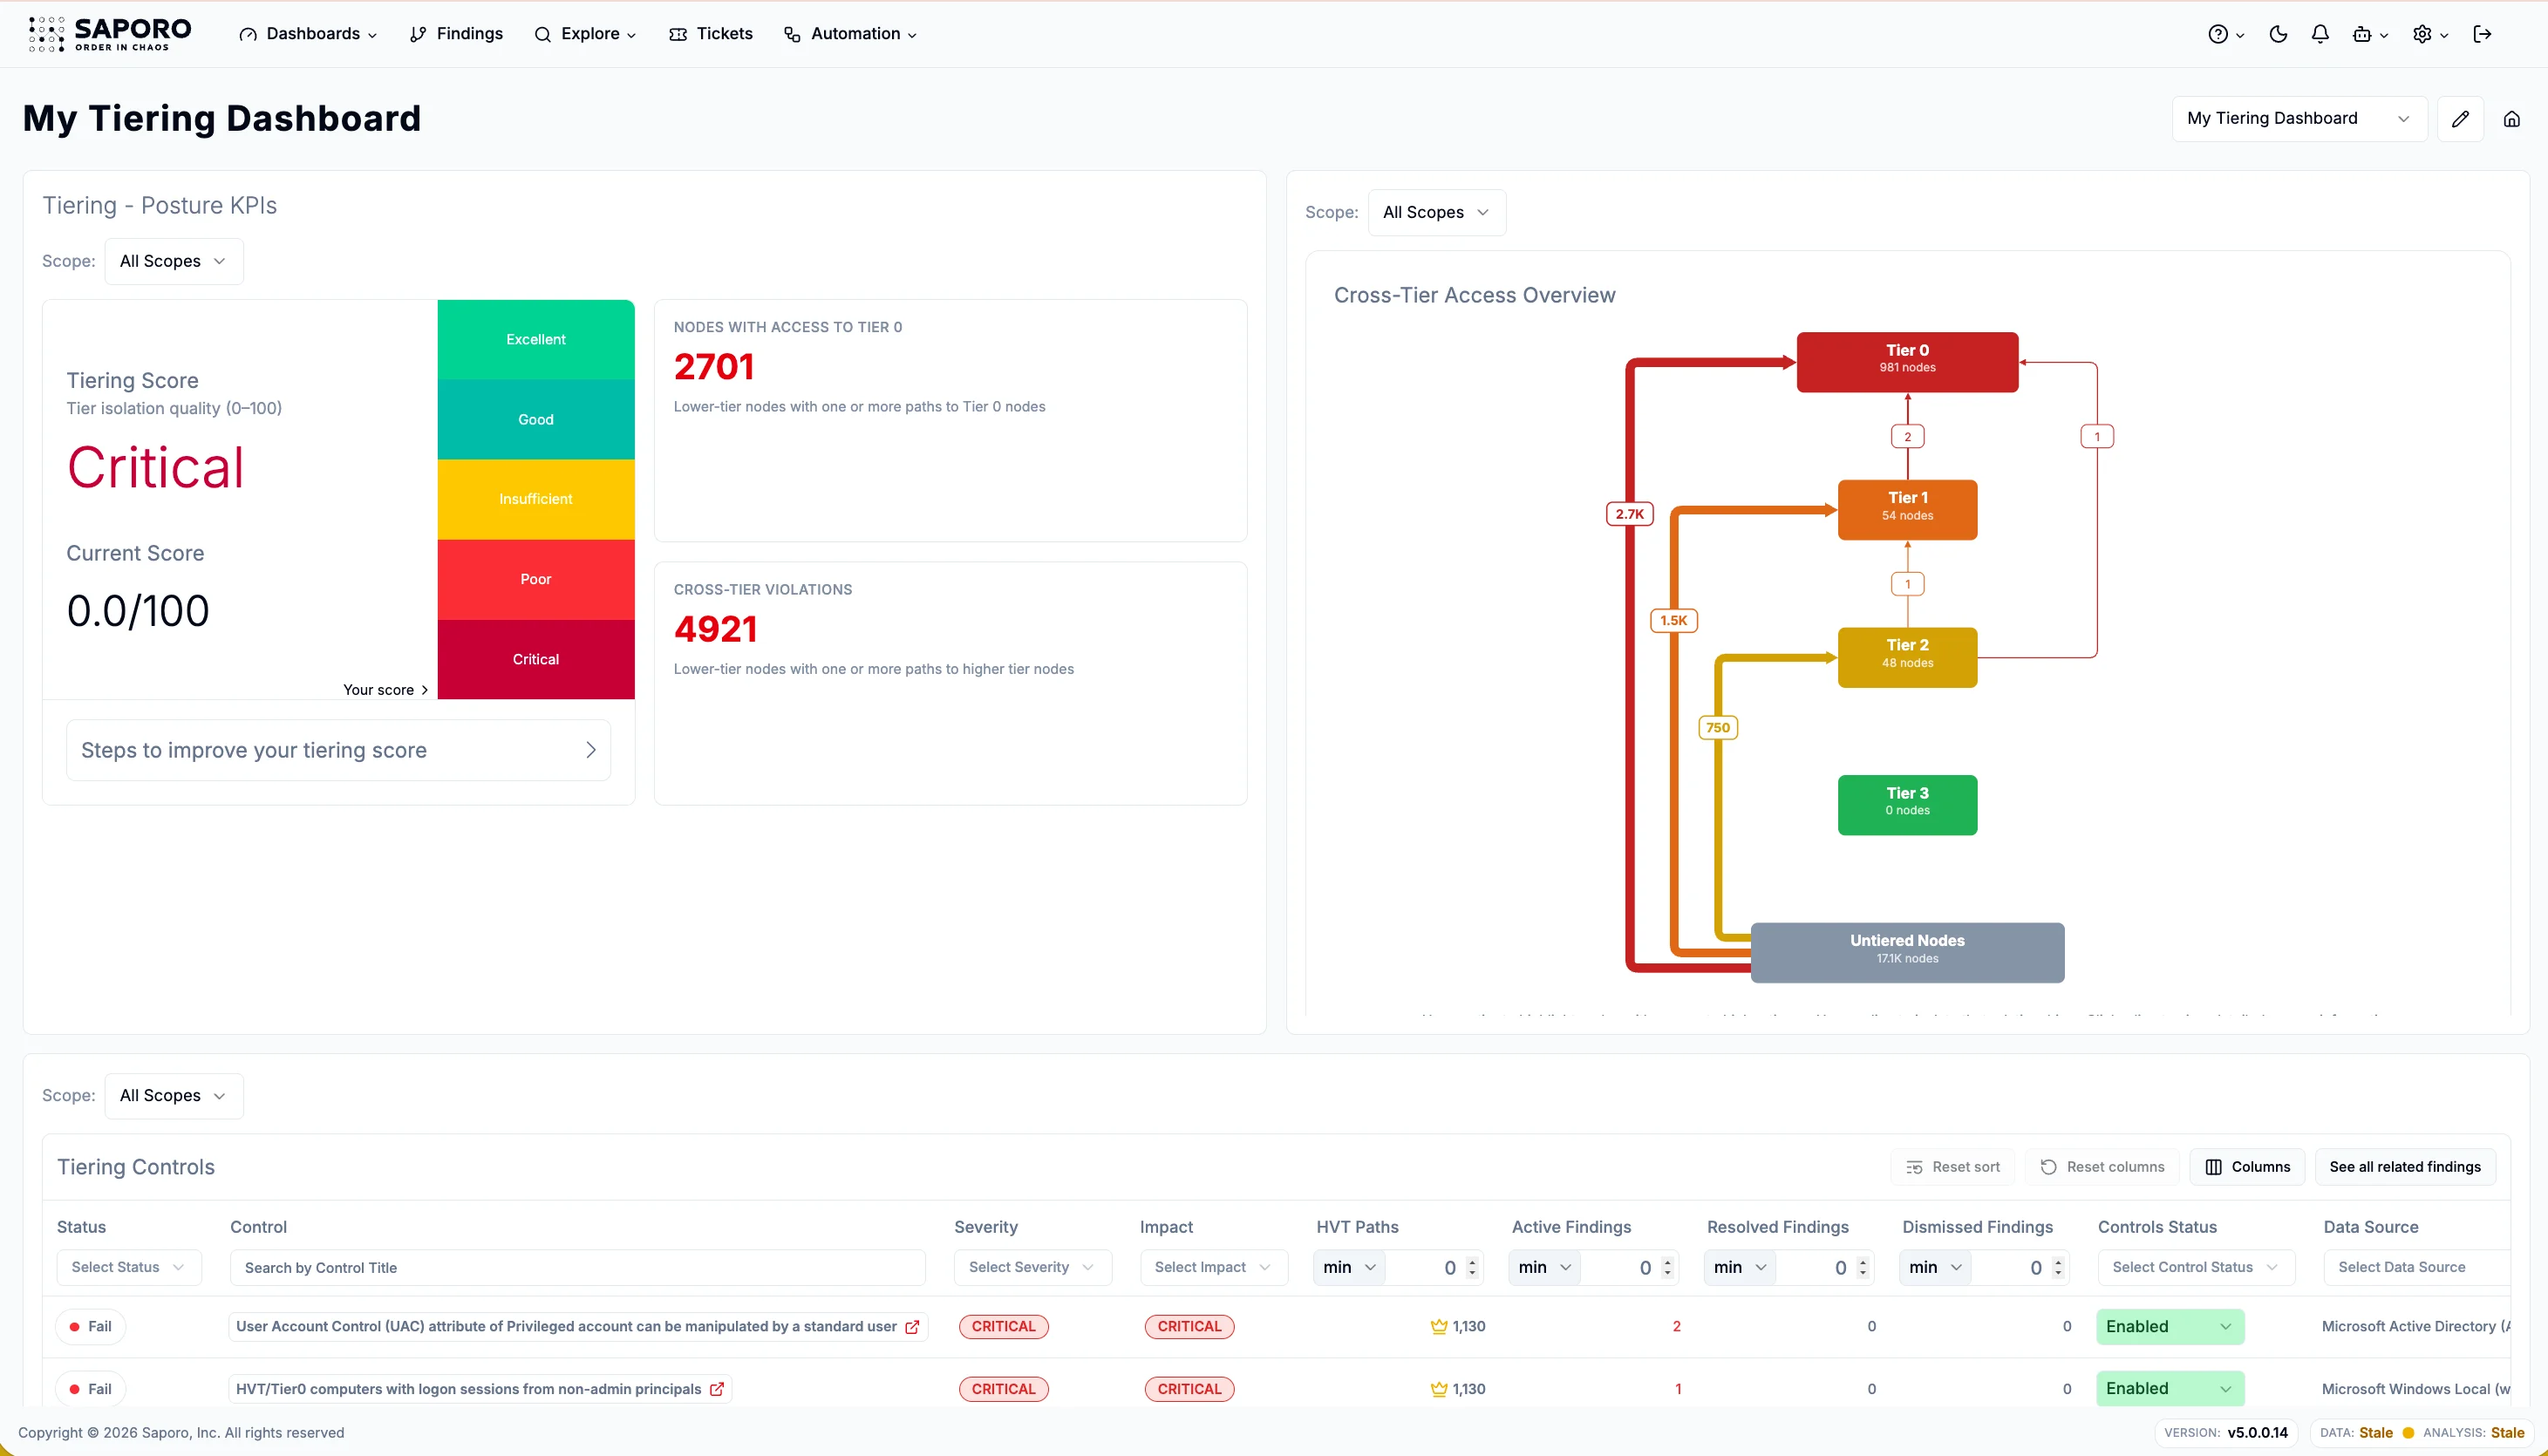
Tier 0
attack paths mapped
The tiering score shows which accounts, groups and delegations cross your tier boundaries to reach Tier 0.
Customer results
Swiss private bank
10M+
Attack paths eliminated
A Swiss private bank mapped 300K+ identities and deployed in under an hour without disrupting banking operations.
“Saporo is an indispensable defense tool for all organizations that want to be one step ahead in controlling risks within their increasingly complex infrastructures.”
French hospital group
Level 1 to 3
ANSSI ORADAD improvement
A major French hospital group eliminated millions of attack paths with no impact on clinical systems.
“Saporo offers a unique view of both misconfigurations from frameworks like ANSSI and attack path evolution, enabling our teams to improve AD security much faster and with less resources.”
Easy on your environment
Guided from setup to results
A Saporo identity engineer works with your team from scoping and setup through the results readout.
The collector uses scoped service identities and read-only access. It can be deployed on-premises or in your cloud, depending on the agreed assessment scope.
No. Saporo does not run payloads or exploit simulations as part of the assessment, and the read-only analysis is designed to have no production impact.
Very little. A short scoping call, read-only access, and a results review. The collector deploys in under an hour, and Saporo handles the analysis.
Deployment is completed in under one hour. The assessment report and prioritized findings are delivered the same day.
A Saporo identity engineer follows up to understand your environment, confirm the assessment scope, and guide you through the next steps.
Free. Read-only. Same-day results.
Start with a short scoping call
Request my free assessment
KuppingerCole Analysts
Sifted 250, 2025
InCyber Forum 2024
Tech4Trust, Trust Valley
Trust Valley Days 2022
ISO 27001 certifiedVerified by AssuranceLab
GDPR compliantEU data protection
ECSO memberEuropean Cyber Security Organization